

About
I built EnvDrop because I was tired of seeing API keys and database passwords flying around in Slack DMs and plain-text emails. We've all done it, "just paste it real quick," and then that secret lives in a chat log forever.
Read full description
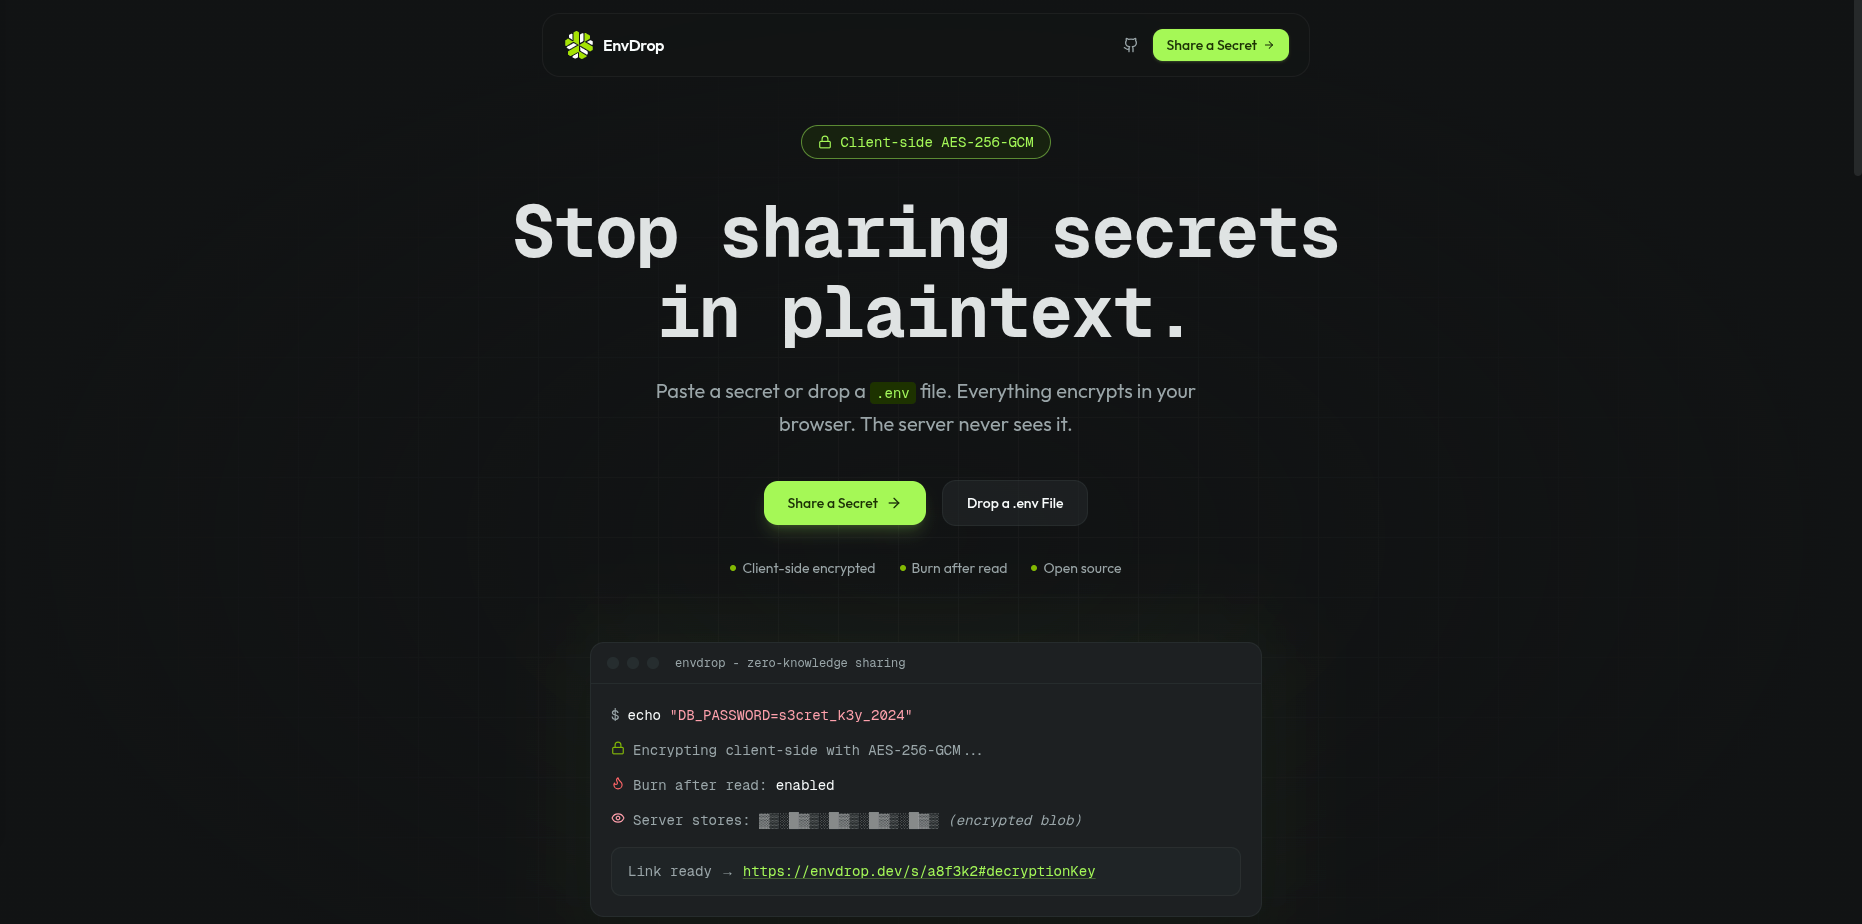
I built EnvDrop because I was tired of seeing API keys and database passwords flying around in Slack DMs and plain-text emails. We've all done it, "just paste it real quick," and then that secret lives in a chat log forever. How it works: - Paste a secret or drop a .env file - Your browser encrypts it with AES-256-GCM before anything leaves your device - You get a one-time link to share - The server never sees the plaintext, ever What makes it different: - True zero-knowledge, encryption keys live in the URL fragment, never sent to the server - Burn after read, the secret self-destructs after one view - Optional password protection for an extra layer - No sign-up, no accounts, no tracking - Fully open source (MIT) I built this with Next.js, Upstash Redis, and @redenv/e2ee encryption library. The entire crypto happens client-side. You can verify it yourself in the source code. Would love your feedback on the UX, security model, or anything else. Happy to answer questions about the architecture!
- Category
- Productivity
- Available on
- web
- Launched
- March 24, 2026
Reviews
No reviews yet. Be the first to share a useful, honest impression.
Sign in to review this app.
Opt in to release updates in your Rocket inbox. Unfollow here or in Notifications to stop future updates.