

LogTide
Open source alternative to Datadog and Splunk. GDPR compliant, self-hosted log management with Sigma rules for threat detection
About
LogTide is an open-source alternative to Datadog, Splunk, and ELK. Designed for developers and European SMBs who need GDPR compliance, data ownership, and simplicity without the complexity of managing an ElasticSearch cluster. Why LogTide?
Read full description
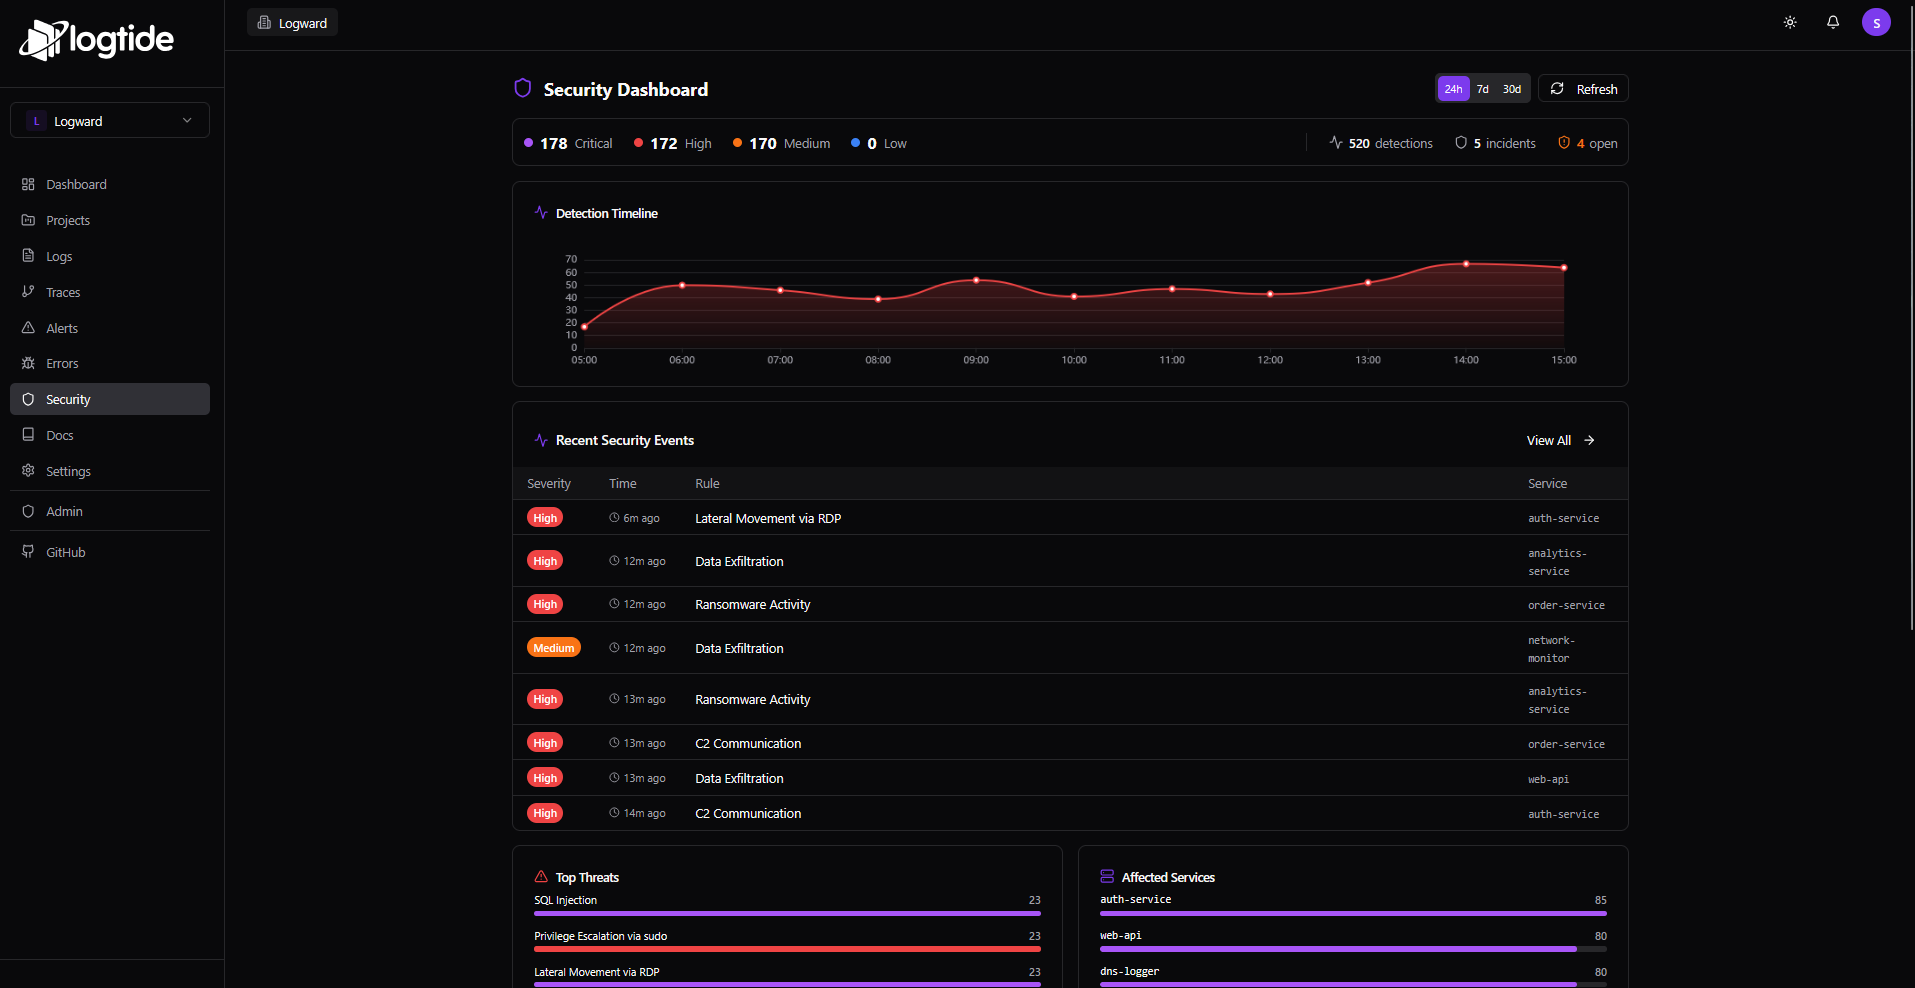
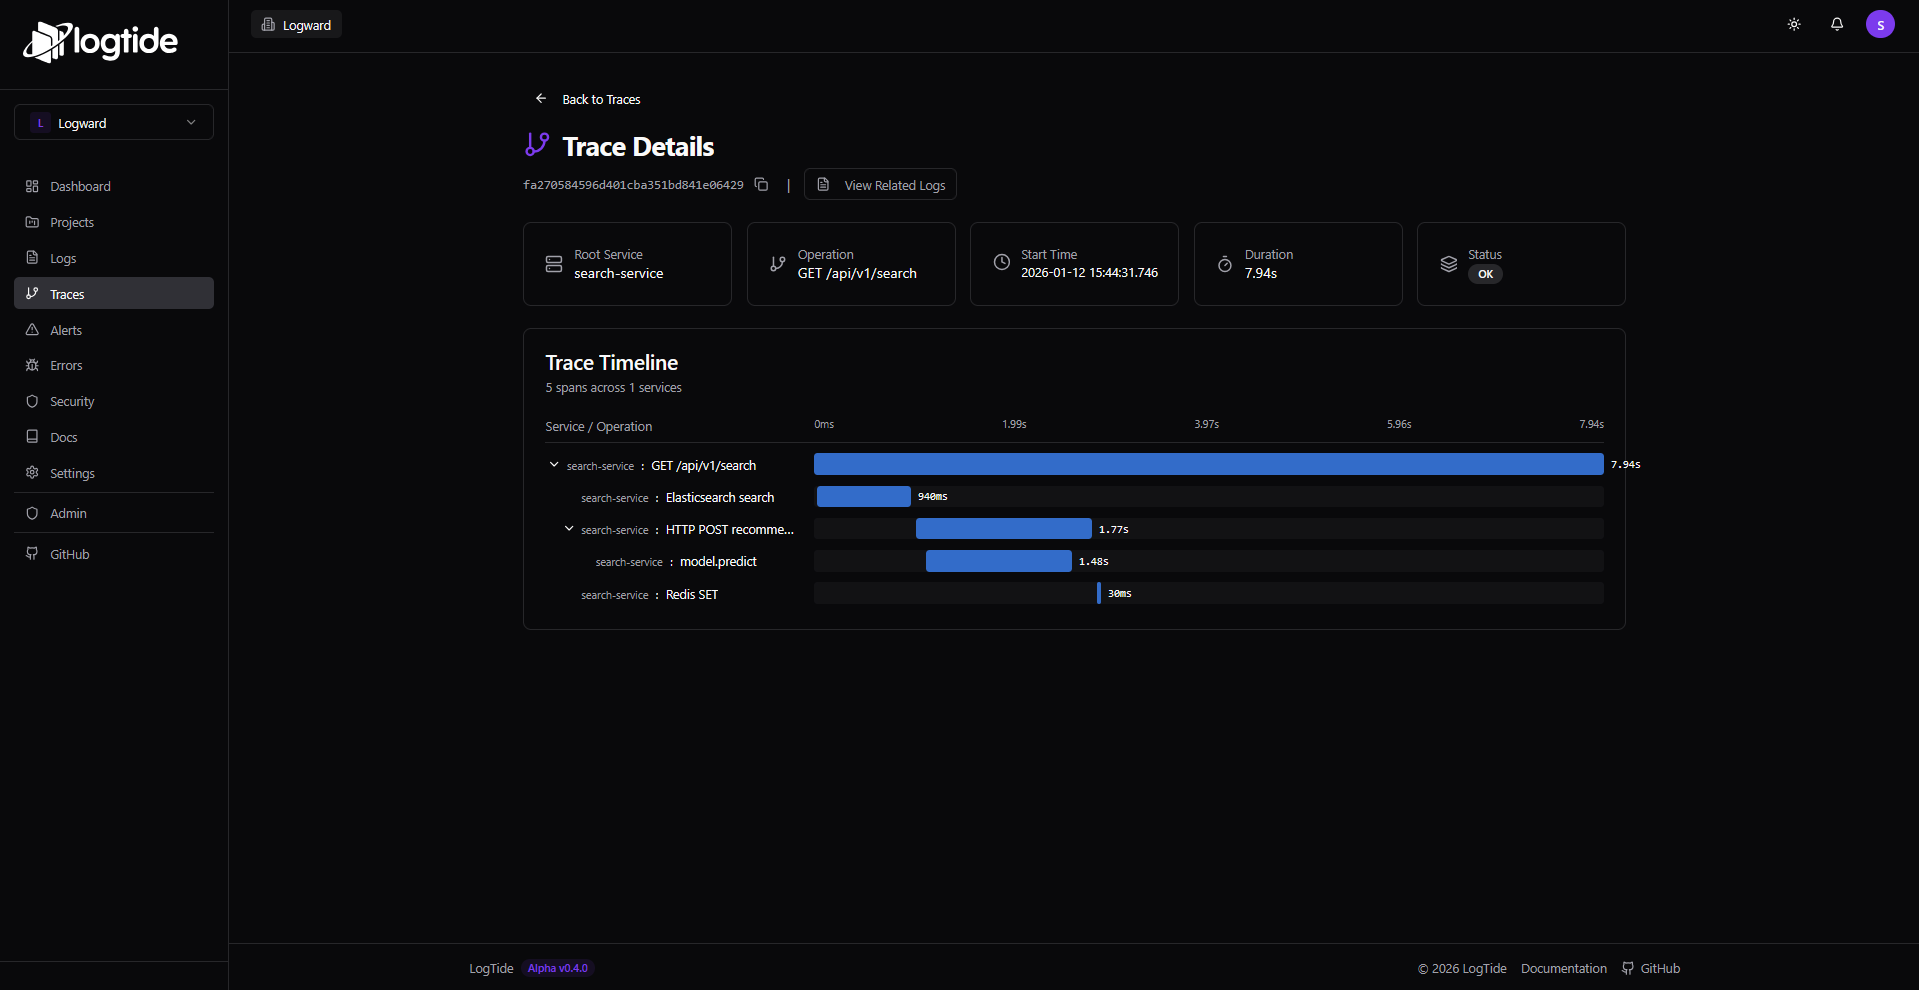
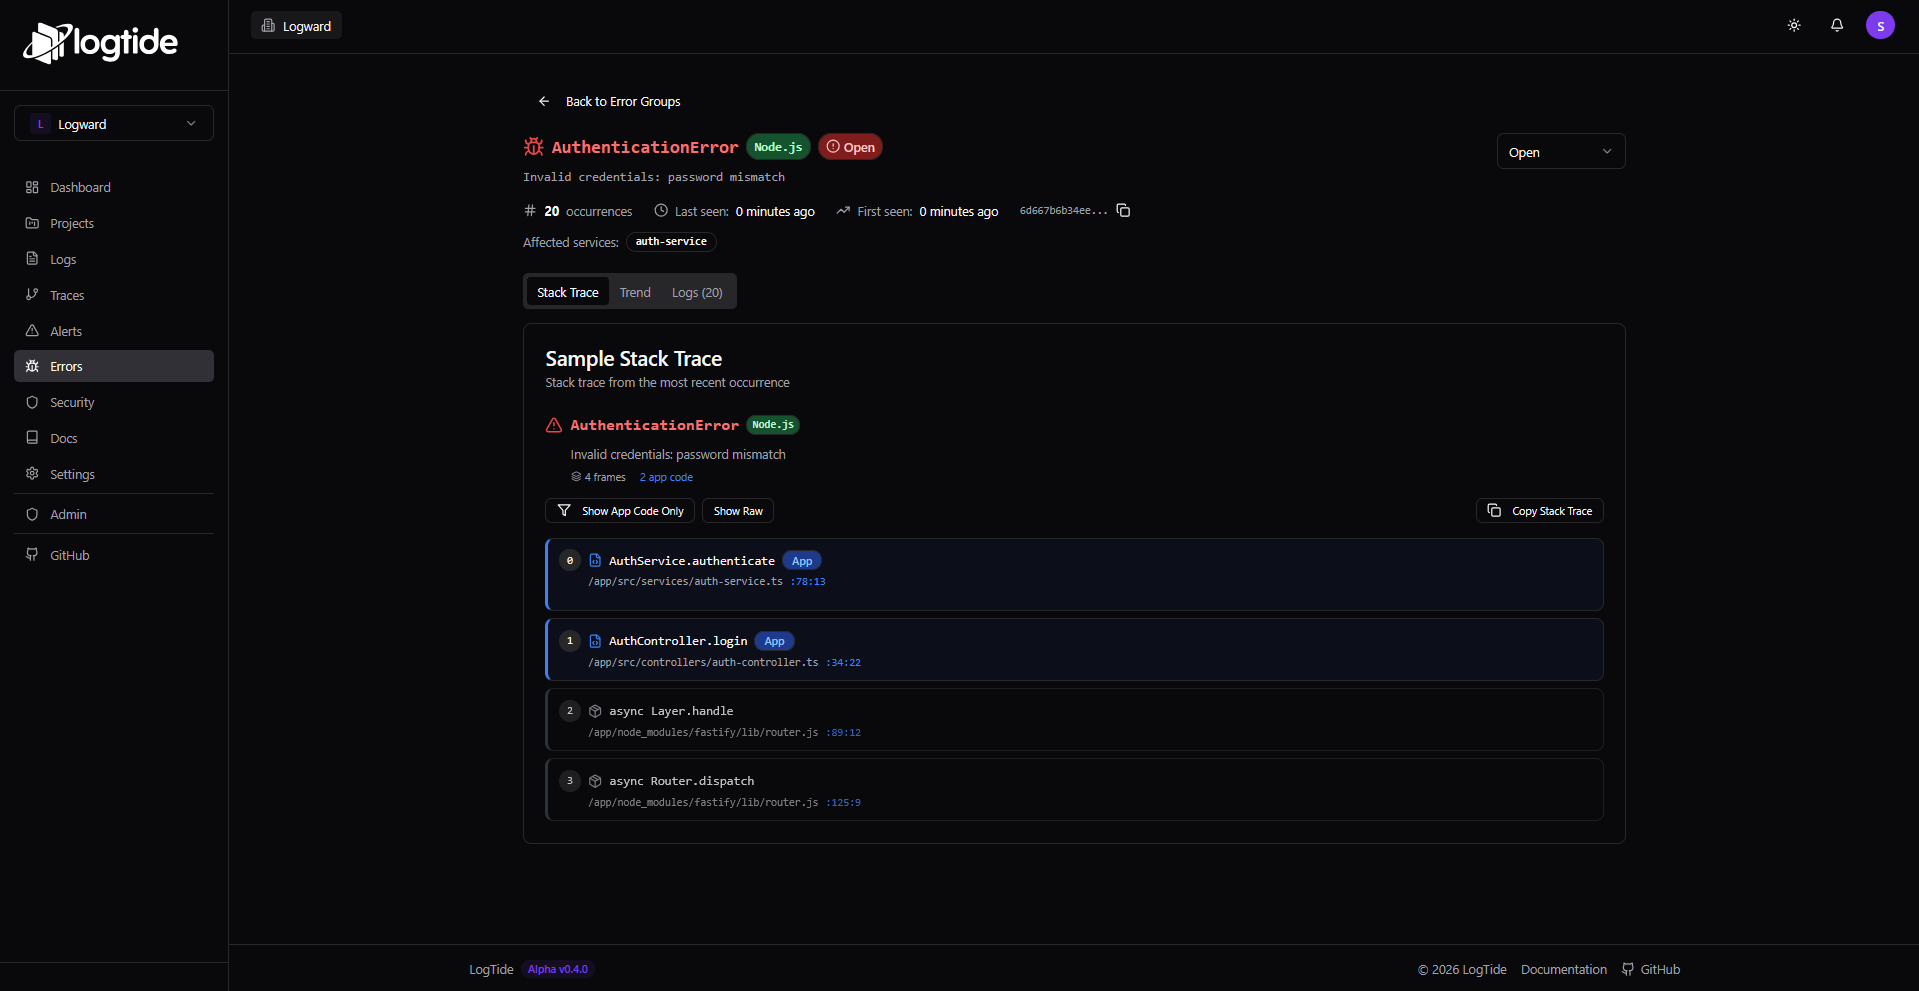
LogTide is an open-source alternative to Datadog, Splunk, and ELK. Designed for developers and European SMBs who need GDPR compliance, data ownership, and simplicity without the complexity of managing an ElasticSearch cluster. Why LogTide? 🇪🇺 GDPR Friendly: Keep data on your servers or use our EU-based cloud. ⚡ Lightweight: Built on TimescaleDB & Fastify (low RAM usage compared to Java stacks). 🚀 Developer Experience: 5-minute setup with Docker. Native SDKs. 💰 Cost Effective: Self-host for free. Features available in Alpha ✅ High-Performance Ingestion: Batch API handling thousands of logs/sec. ✅ Real-time Live Tail: See logs as they arrive via Server-Sent Events (SSE). ✅ Powerful Search: Filter by service, level, time range. Two search modes: Full-text (word-based with stemming) and Substring (find text anywhere in messages, e.g., find "bluez" in "spa.bluez5.native"). ✅ Multi-Organization: Isolate teams and projects strictly. ✅ Alerting: Get notified via Email or Webhook (Slack/Discord) on error spikes. ✅ Retention Policy: Automatic cleanup of old logs via TimescaleDB. ✅ Sigma Rules Detection: Built-in engine to run security detection rules (YAML) against your logs for threat detection. ✅ SIEM Dashboard: Security dashboard with incident management, MITRE ATT&CK mapping, and PDF report export. ✅ OpenTelemetry Support: Native OTLP ingestion for logs and traces (protobuf + JSON). ✅ Distributed Tracing: Trace viewer with span timeline, service dependencies graph, and trace-to-logs correlation. ✅ Redis Optional: Run without Redis using PostgreSQL-based alternatives for simpler deployments. ✅ Detection Packs: Pre-configured Sigma rule bundles for common security use cases. ✅ Event Correlation: Link related logs by request_id, trace_id, user_id, or custom fields. ✅ Alert Preview: Test alert rules against historical data before enabling them.
- Category
- Data analysis tools, Engineering & Development, Productivity
- Available on
- web
- Launched
- February 22, 2026
Reviews
No reviews yet. Be the first to share a useful, honest impression.
Sign in to review this app.
Opt in to release updates in your Rocket inbox. Unfollow here or in Notifications to stop future updates.